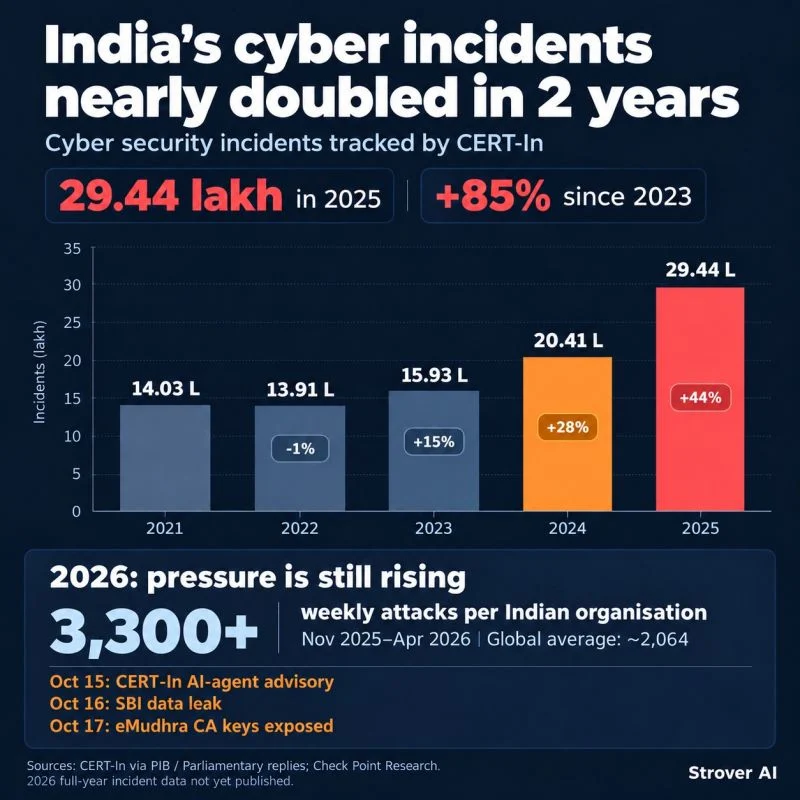
15 Oct: CERT-In warned of AI agents accessing Indian organisations’ live systems. None of the organisations in the voluntarily disclosed cases detected the access themselves.
16 Oct: SBI received alerts about customer data on the dark web. Its preliminary review identified 3,897 customer records. The source remains under investigation.
17 Oct: A researcher reported eight weak eMudhra certificate-signing keys. Google and Mozilla blocked the affected certificates within hours.
These are separate events. No public evidence links SBI’s exposure to AI.
Meanwhile, cyber incidents reported to and tracked by CERT-In rose from 15.9 lakh in 2023 to 29.4 lakh in 2025—an 85% increase.
For security leaders, three questions:
- Do we know where our secrets and keys are?
- Do we know which APIs and cloud resources are exposed?
- Can we prove our fixes worked?
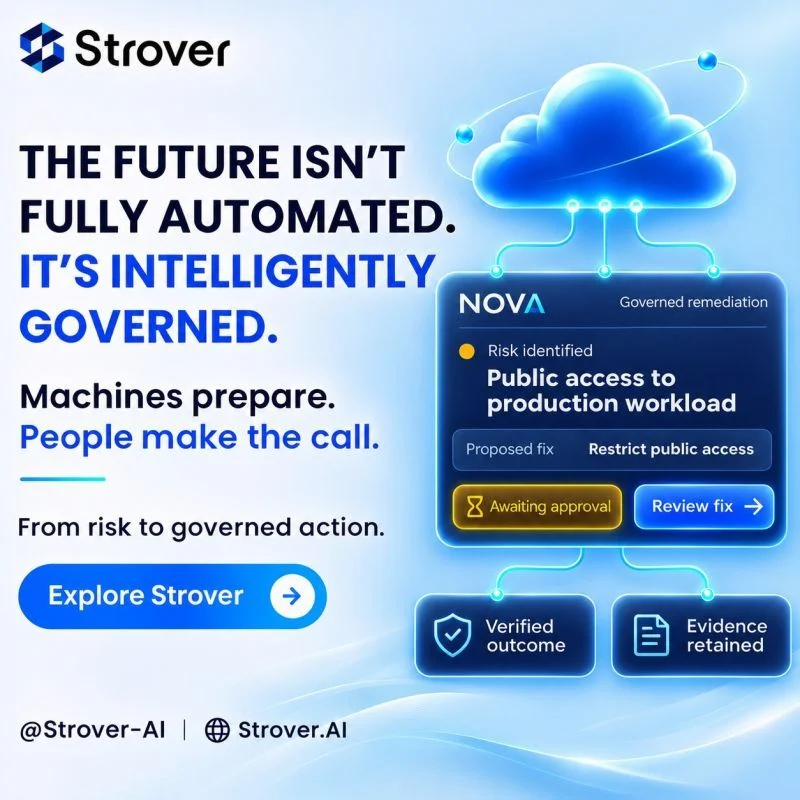
At Strover AI, these questions guide our work on cloud exposure, governed remediation and audit-ready evidence.
Visibility first. Then remediation you can verify.