 Carousel · 5 pages
Ask a security team how many tools they use and you’ll usually get a long list.
Ask who connects them and you’ll often get a pause.
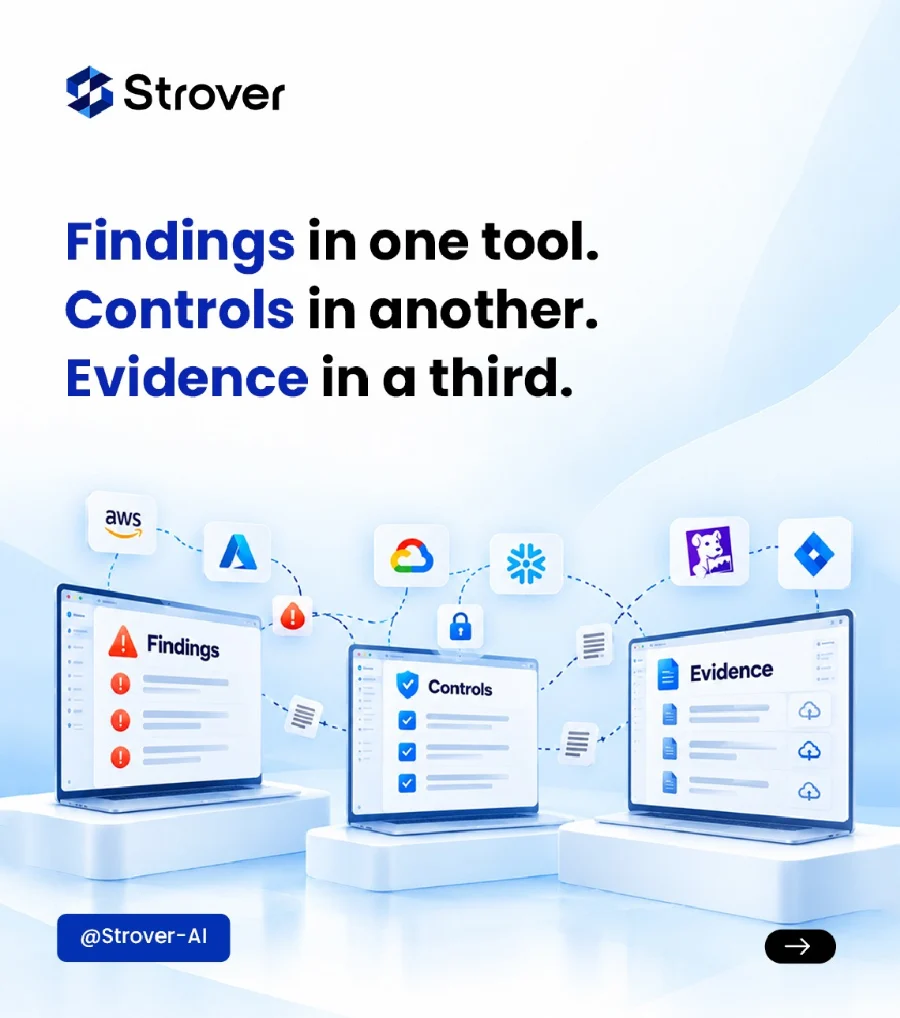
When findings, compliance controls and audit evidence live in separate places, analysts end up as the integration layer: matching duplicate alerts, adding business context, chasing owners by hand.
Strover takes on that work.
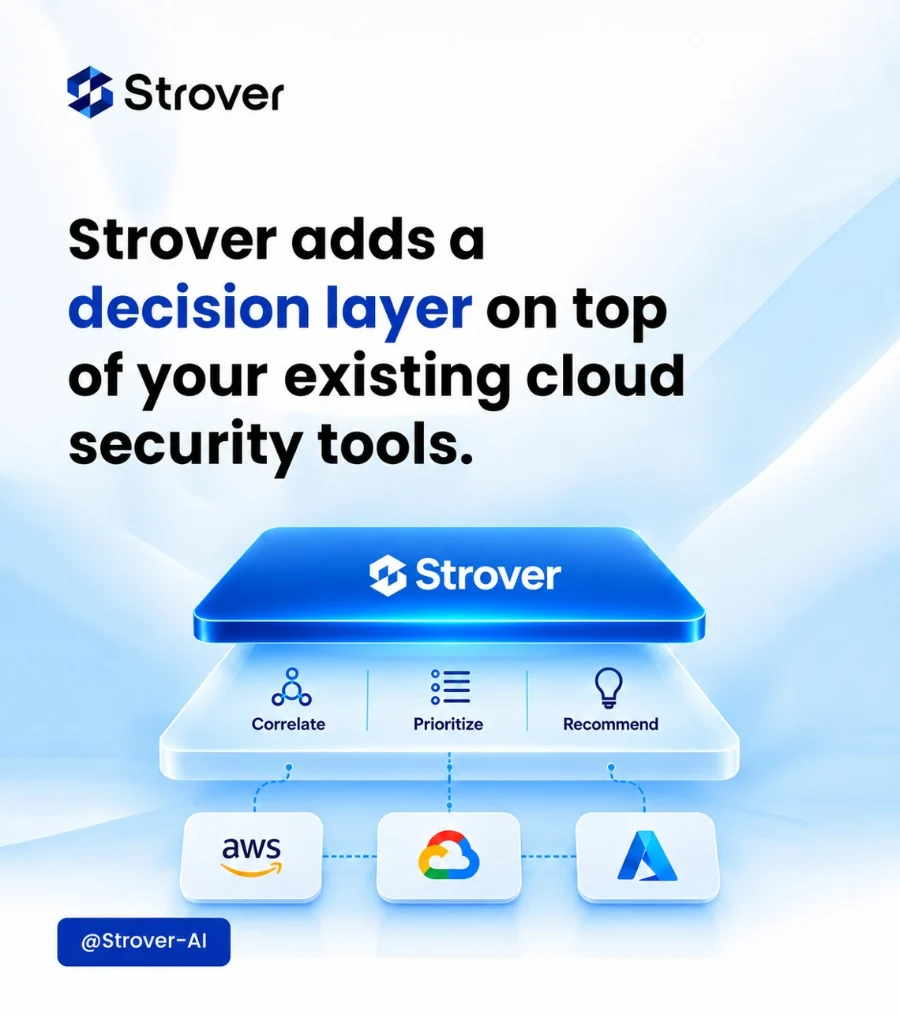
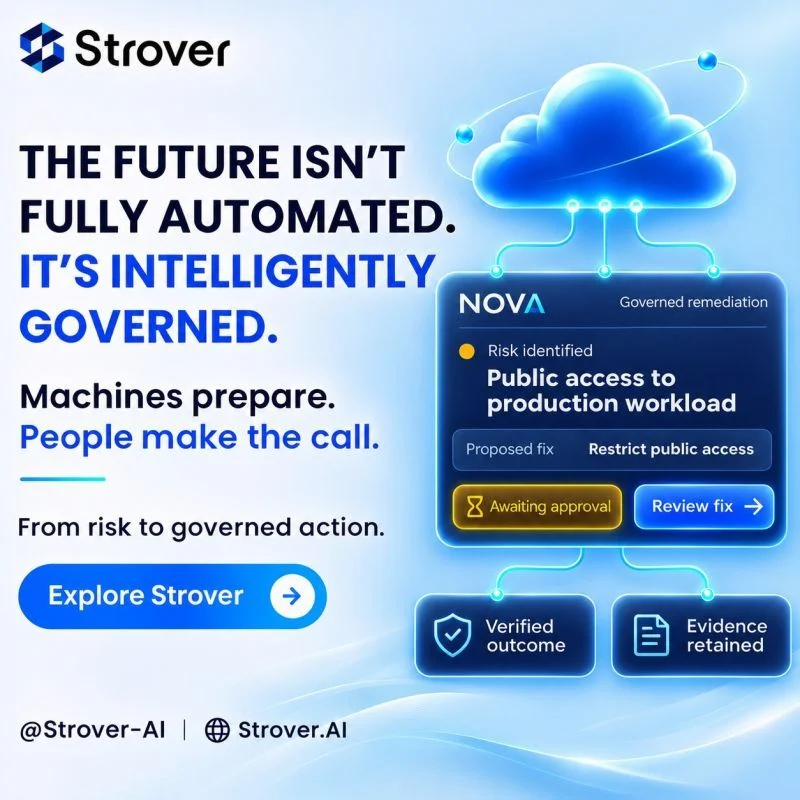
It sits on top of your existing cloud security services, correlates what each one already reports, and ranks findings by what’s actually at stake. Each finding then moves through approval, remediation and verification as one traceable case.
Your team spends its time deciding, not stitching data together.
Nothing needs replacing. Every action stays human-approved and audit-ready.
Which gap between your tools slows your team down most? Tell me below.
More from the carousel
“Your Cloud Security Tools Aren’t the Problem” · 5 pages on LinkedIn