 Carousel · 5 pages
Most cloud risks don’t stay open because they were missed. They stay open because the path from finding to fix is split across tools and teams.
One tool raises the alert. Another tracks the ticket. Someone else approves the change.
Evidence gets rebuilt later for the audit. At every handoff, ownership gets fuzzy.
Which handoff breaks first on your team? Vote below, and tell me why in the comments.
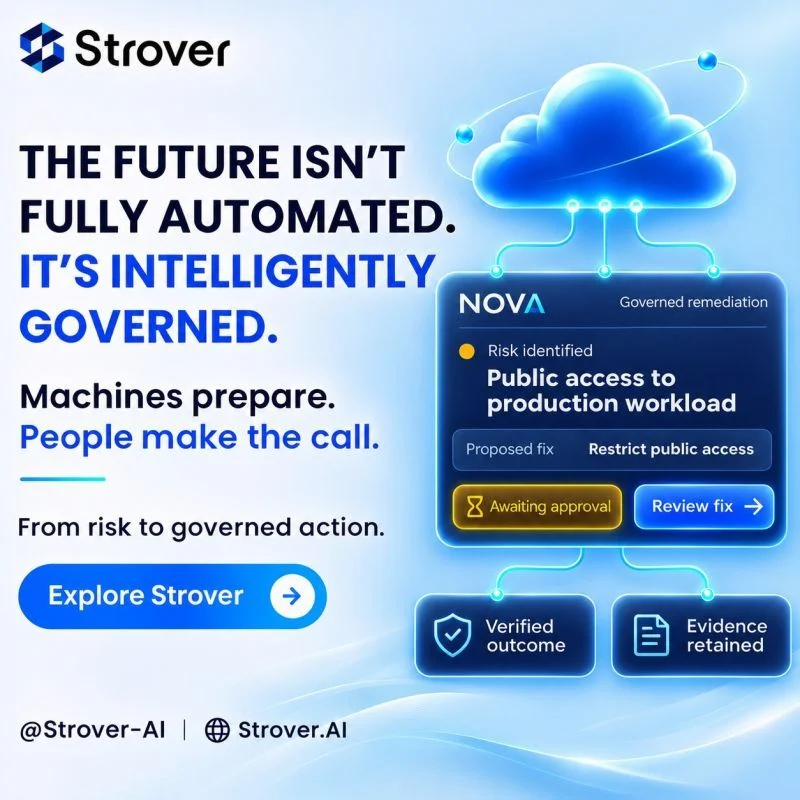
That gap is why we built Strover. It correlates findings and adds business context, so teams know what needs attention first. Each risk becomes one governed case:
- a clear owner
- a proposed fix
- human approval before anything changes
- verification once it’s done
- an audit-ready evidence trail
It sits on top of the security tools you already use. Nothing to rip out.
More from the carousel
“Who Owns the Risk When Everyone Sees It?” · 5 pages on LinkedIn
#Cybersecurity#CloudSecurity#RiskManagement#CyberRisk#InformationSecurity#CloudComputing#DevSecOps#SecOps